WSO2 is now Choreo LabsLearn more

Trusted AI Governance
Build

Create agents and AI apps with the tools and languages your teams already use.

Connect

Link agents securely to your APIs, data, models and business systems.

Run

Deploy, observe and operate agents and AI apps reliably at any scale.

Govern

Control identity, access, cost and policy for every agent in production.

Agent Management

Developer Platform

  • API Management Cloud

    Design, secure and publish APIs with governance and analytics built in.

    Sign Up Now
  • Integration Cloud

    Connect apps, data and AI agents with low-code and pro-code integration.

    Sign Up Now
  • Identity & Access Management Cloud

    Secure sign-in and access for customers, partners, workforce and agents.

    Sign Up Now
  • Agent Management Cloud

    Build, run and govern AI agents with full visibility and control.

    Sign Up Now
  • Developer Platform Cloud

    Ship cloud-native apps faster on an internal developer platform.

    Sign Up Now

Self-Hosted

Full control over your stack. Deploy directly to your own servers, bare metal, cloud, or Kubernetes environment. Your data never leaves your perimeter.

Product Downloads
Choreo Labs
AI Governance
Platform
Solutions
Resources

Choreo Labs Changelog

ImprovementAsgardeo

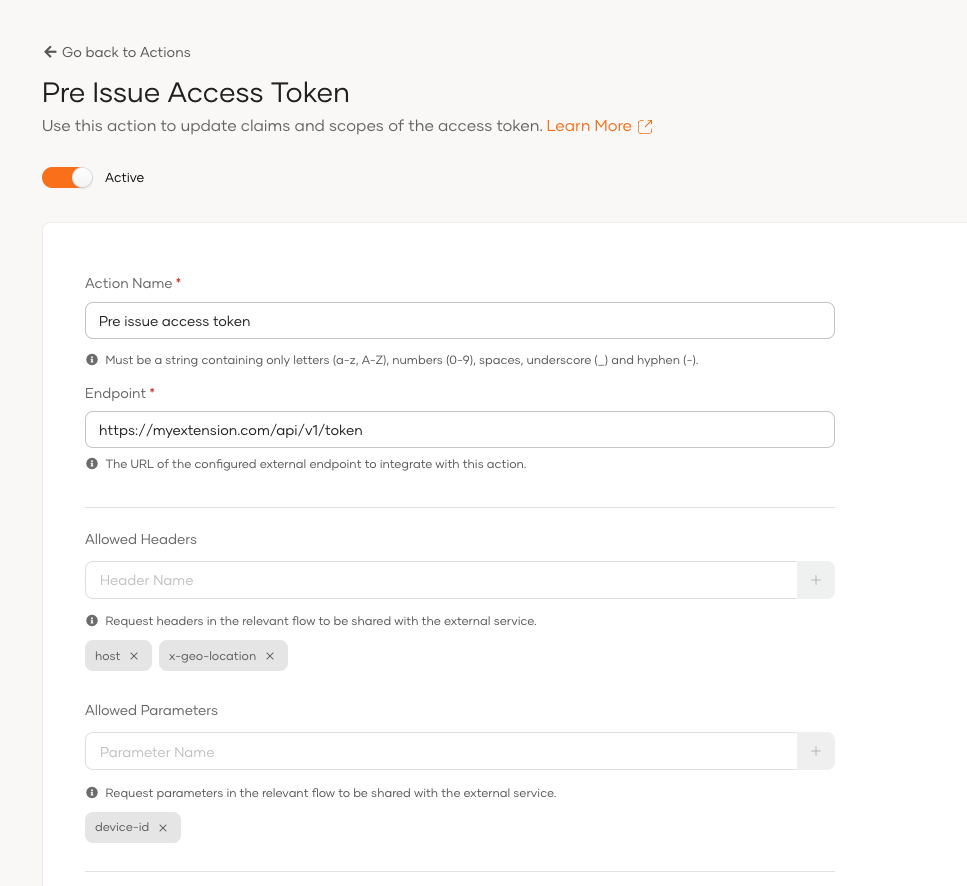
Configure allowed headers and parameters to be shared with pre-issue access token extension and custom authenticator (service-based)

In extension points such as Pre-Issue Access Token and Custom Authenticator actions, it is common to rely on additional headers and parameters from the request flow. However, allowing unrestricted access to all headers and parameters poses security risks, as they may contain sensitive information, personally identifiable data (PII), or internal infrastructure details.

Now the extension developers can explicitly select which headers and parameters should be shared with the extension, in addition to the safeguards already applied at the server level. This ensures extensions get the required data while maintaining strong security controls.
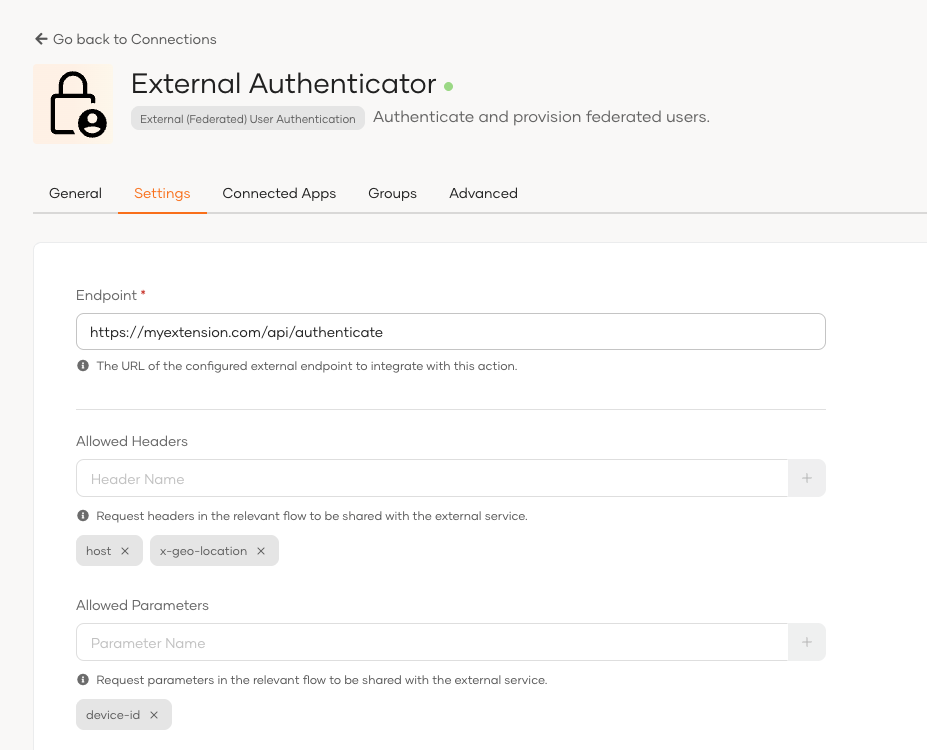
External AuthenticatorExternal Authenticator screenshott

Documentation: