WSO2 is now Choreo LabsLearn more

Trusted AI Governance
Build

Create agents and AI apps with the tools and languages your teams already use.

Connect

Link agents securely to your APIs, data, models and business systems.

Run

Deploy, observe and operate agents and AI apps reliably at any scale.

Govern

Control identity, access, cost and policy for every agent in production.

Agent Management

Developer Platform

  • API Management Cloud

    Design, secure and publish APIs with governance and analytics built in.

    Sign Up Now
  • Integration Cloud

    Connect apps, data and AI agents with low-code and pro-code integration.

    Sign Up Now
  • Identity & Access Management Cloud

    Secure sign-in and access for customers, partners, workforce and agents.

    Sign Up Now
  • Agent Management Cloud

    Build, run and govern AI agents with full visibility and control.

    Sign Up Now
  • Developer Platform Cloud

    Ship cloud-native apps faster on an internal developer platform.

    Sign Up Now

Self-Hosted

Full control over your stack. Deploy directly to your own servers, bare metal, cloud, or Kubernetes environment. Your data never leaves your perimeter.

Product Downloads
Choreo Labs
AI Governance
Platform
Solutions
Resources

Choreo Labs Changelog

FeatureAsgardeo

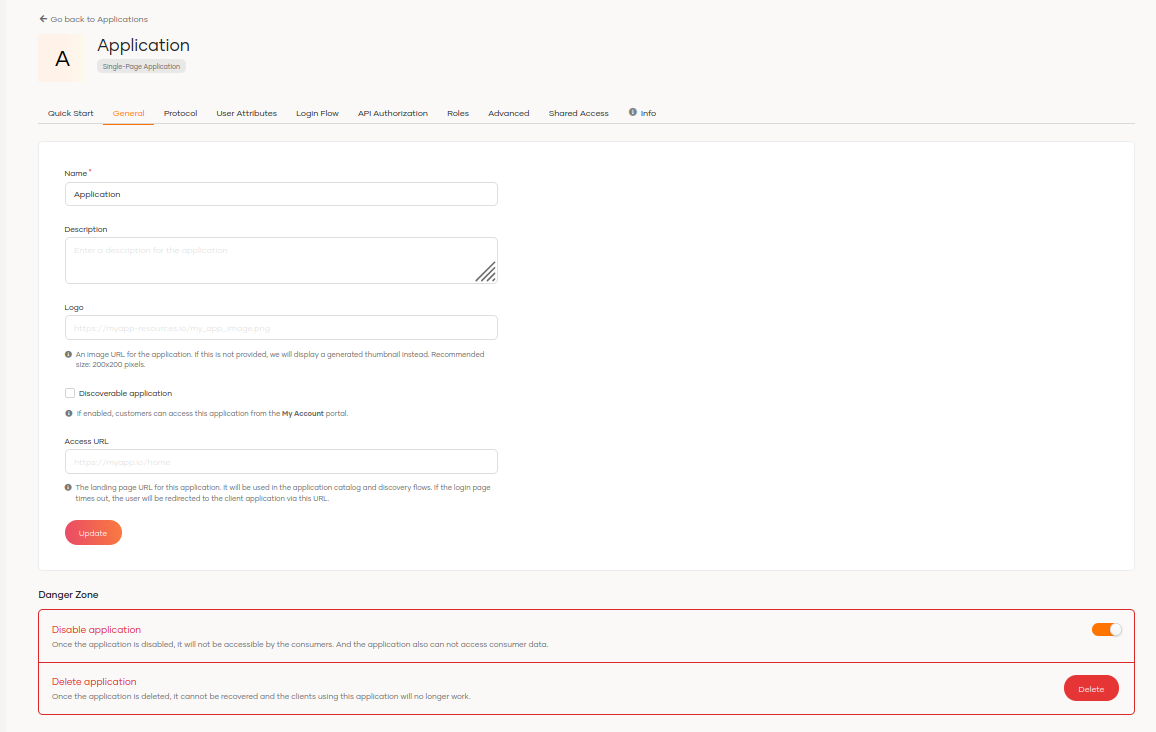
Capability to disable an application

We are excited to announce a significant update aimed at enhancing the security and integrity of our application and improving ongoing maintenance processes.
Organizations today face constant risks from potential cyber attacks that can lead to unauthorized access to sensitive information. Such incidents jeopardize the privacy and security of both the organization and its users. To proactively mitigate these risks, we are implementing the following measures:

  • Disabling Access to Compromised Applications/Maintenance
  • Preventing Access to User Information: While we already take steps to protect user information, this new feature introduces an additional layer of security. Specifically, when the application is disabled or undergoing maintenance, it will no longer be able to access user information—even if the user has previously given consent.
  • Token Invalidation: Invalidate all previously issued tokens (e.g., JWTs) to ensure they can no longer be used to authenticate requests.

Documentation: