

Improve customer experience and API security with WSO2 Identity Server 7.0
This guest blog was written by Inetum, a valued partner and reseller of WSO2 products
In today’s digital world, APIs have become key to connect apps and services, both internally and externally. However, when integrating with external entities like partners and service providers, API security is a major concern for businesses. And from a user’s perspective, traditional authentication approaches in mobile apps or digital channels often deliver a less-than-ideal digital experience. Inetum, an expert in WSO2 products and a value added reseller, relies on WSO2’s industry-leading offerings to help our enterprise customers to overcome these challenges. Consider the two following examples to see why the latest WSO2 Identity Server release is best suited for today’s demands.
Use Case 1: Improving API Security
Many of our customers and partners contact us to set up WSO2 API Manager and integrate it with their digital channels (like mobile applications, selfcare portals, e-shops, etc.). As mentioned before, a key challenge is to ensure API security, while providing a seamless user experience.
WSO2 Identity Server 7.0 comes with a range of advanced features for API security, which helps us to meet customer requirements and expectations across different sectors (e.g., finance, government, telco, retail). Some important features include the following:
- OAuth 2.0 and OpenID Connect: Standardized authentication and authorization for APIs.
- Scopes and RBAC: Granular control of API access based on roles and scopes.
- Push Authorization Requests (PAR): Useful for securing mobile APIs and will ensure:
- That the integrity of the query is protected.
- The confidentiality of the request.
- Allows you to pass complex queries without browser limitations.
- Avoids infiltration of query strings to third-party sites and web server logs.
- JARM: OAuth2 Security Enhancement.
- FAPI 1.0: API Compliance with Financial Security Standards:
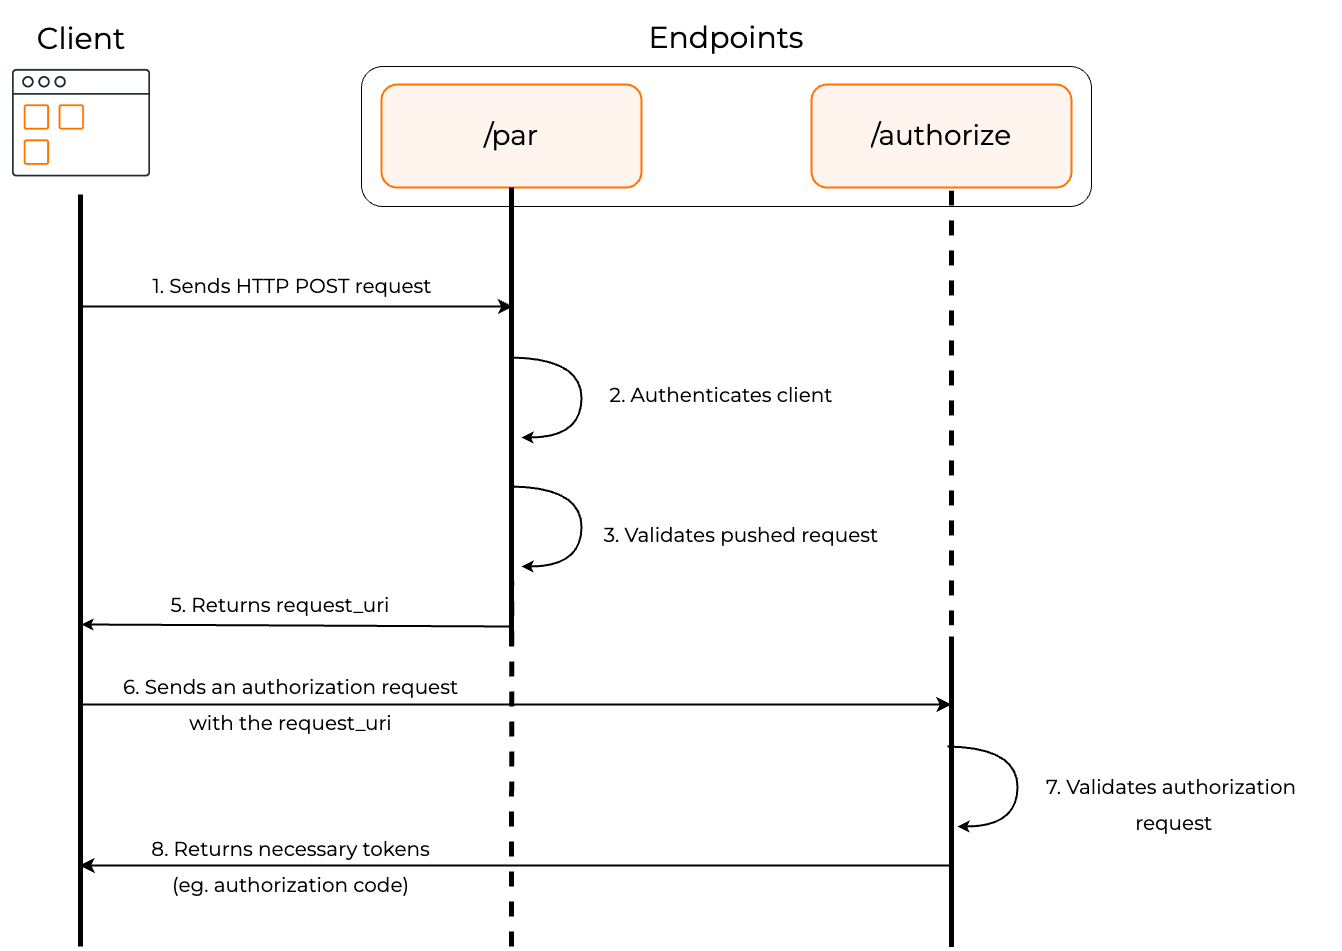
For more details, please refer to the following documentation link: https://is.docs.wso2.com/en/next/references/pushed-authorization-requests/
Financial-grade API (FAPI), a specification that extends the OAuth and OIDC frameworks, was introduced by the FAPI Working Group and defines additional technical requirements for securing APIs. Although FAPI was originally defined for financial services, this security mechanism is also valid for any critical API where security is the highest priority.
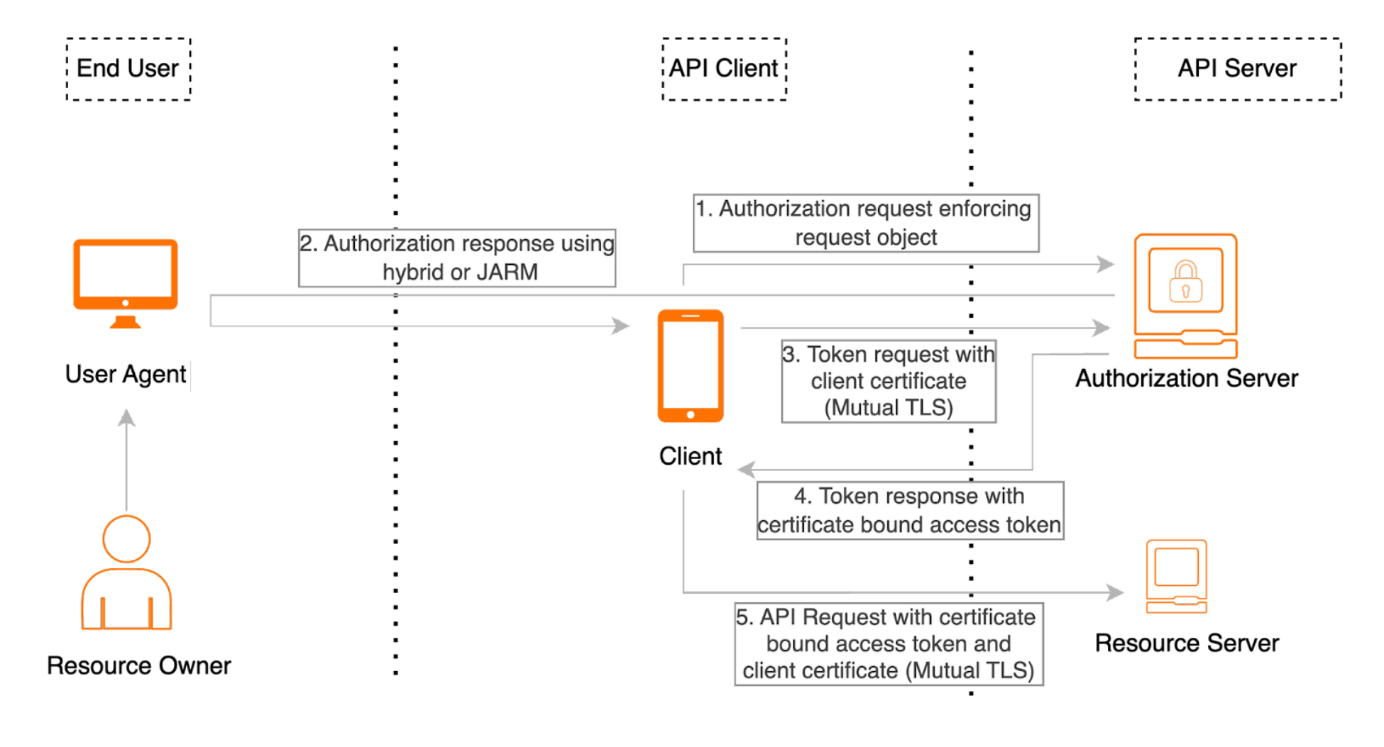
For more details, please refer to the following documentation link: https://is.docs.wso2.com/en/next/references/financial-grade-api/
To summarize ,WSO2 Identity Server helps our customers to:
- Improve and strengthen the security of their APIs.
- Reduce the risk of fraud and hacking.
- Comply with industry-specific safety regulations.
Use Case 2: Deliver a Seamless Customer Experience with App-Native Authentication
Traditional authentication approaches, which redirect users to a web browser, can detract from the customer experience in mobile apps. Our clients often tell us about this and the issues users have to face when logging in.
With WSO2 Identity Server 7.0, we can now easily overcome this challenge and improve the customer journey with app-native authentication, an extension of the OAuth 2.0 protocol that allows users to authenticate to native mobile apps without being redirected to a web browser.
For more details, on how to secure native authentication requests, please refer to the following documentation link: https://is.docs.wso2.com/en/next/references/app-native-authentication/
Now, users can authenticate directly in the mobile app, without leaving the interface. This provides a smooth and intuitive experience. Users can now connect seamlessly and securely, without interruption.
In addition to basic authentication, using WSO2 Identity Server 7.0, you can also implement Native App Multi factor Authentication MFA for increased security.
As shown here, WSO2 Identity Server 7.0 secures APIs and boosts customer experience. To learn more, we encourage you to visit the official product page.
.