

WSO2 Agentic Enterprise fabric
WSO2 Agentic Enterprise Fabric (AEF) is the architectural foundation for running AI agents safely at enterprise scale, bringing together the API, integration, identity, engineering, and agent platforms into one coherent model for building, connecting, governing, and operating agents.
About the Internship
As a Cybersecurity Intern, you'll gain hands-on experience working alongside our Governance, Risk, and Compliance (GRC) team, contributing to initiatives across security, compliance, risk management, privacy, and data protection. You'll collaborate with technical, business, and leadership teams while supporting security and compliance efforts that enable WSO2 to serve customers in over 100 countries. This internship offers a unique opportunity to develop practical skills, work on meaningful projects, and learn from experienced cybersecurity professionals.
What You'll Learn
- Hands-on exposure to ISO, PCI-DSS, SOC 2, and other globally recognised certification and attestation programs.
- Understanding on how audit controls are designed, executed, and evidenced.
- Supporting external audits and evidence gathering across multiple teams.
- Understanding risk management methodologies and managing risk registers across multiple product offerings and business units.
- Planning and tracking security and compliance activities across multiple business units via dashboards and follow-ups.
- Principles and concepts relating to data privacy and data protection.
- Global regulations and concepts on data privacy and data protection and how they can be applied in real-life scenarios.
- Understanding of third-party and supplier risk management, including security assessments, compliance reviews, and ongoing monitoring of vendors and sub-processors.
- Collaboration with legal, risk, engineering, product, and operations teams to embed security and privacy requirements into business processes and product development lifecycles.
- Development of skills to translate technical and regulatory requirements into business-friendly guidance for diverse stakeholders.
- Learning how to balance regulatory compliance with business agility and operational efficiency, using a risk-based and pragmatic approach.
- Building strong foundations for professional certifications and long-term career growth in cybersecurity governance, risk, compliance, and data protection.
Key Requirements
- Pursuing a degree in Cybersecurity or equivalent.
- Basic understanding of technical compliance requirements and standards.
- Interest in technical troubleshooting, technical documentation, and project management.
- Ability to multi-task across multiple initiatives and teams.
- Strong interpersonal skills to communicate requirements and findings across multiple functional teams.
- The drive to excel and a never-give-up attitude.
- Curiosity and eagerness to learn and explore.
- Ability to work both independently and collaboratively in a fast-paced environment.
- Basic familiarity with documentation tools, spreadsheets, and collaboration platforms (e.g., Google Workspace, Github) is an advantage.
Diversity Drives Innovation:
We've built our business on a commitment to diversity and inclusion. We believe it's important to foster an environment that values and respects each individual's strengths, perspectives, and ideas. Doing so not only drives innovation; it also ensures that we can create superior experiences for our customers, partners, and employees worldwide. We value the diversity of our team regardless of race, ethnicity, religion, gender, age, national origin, disability, sexual orientation, or veteran or marital status, and we do not tolerate any form of discrimination.
Choreo Labs Changelog
- 17 Nov, 2026
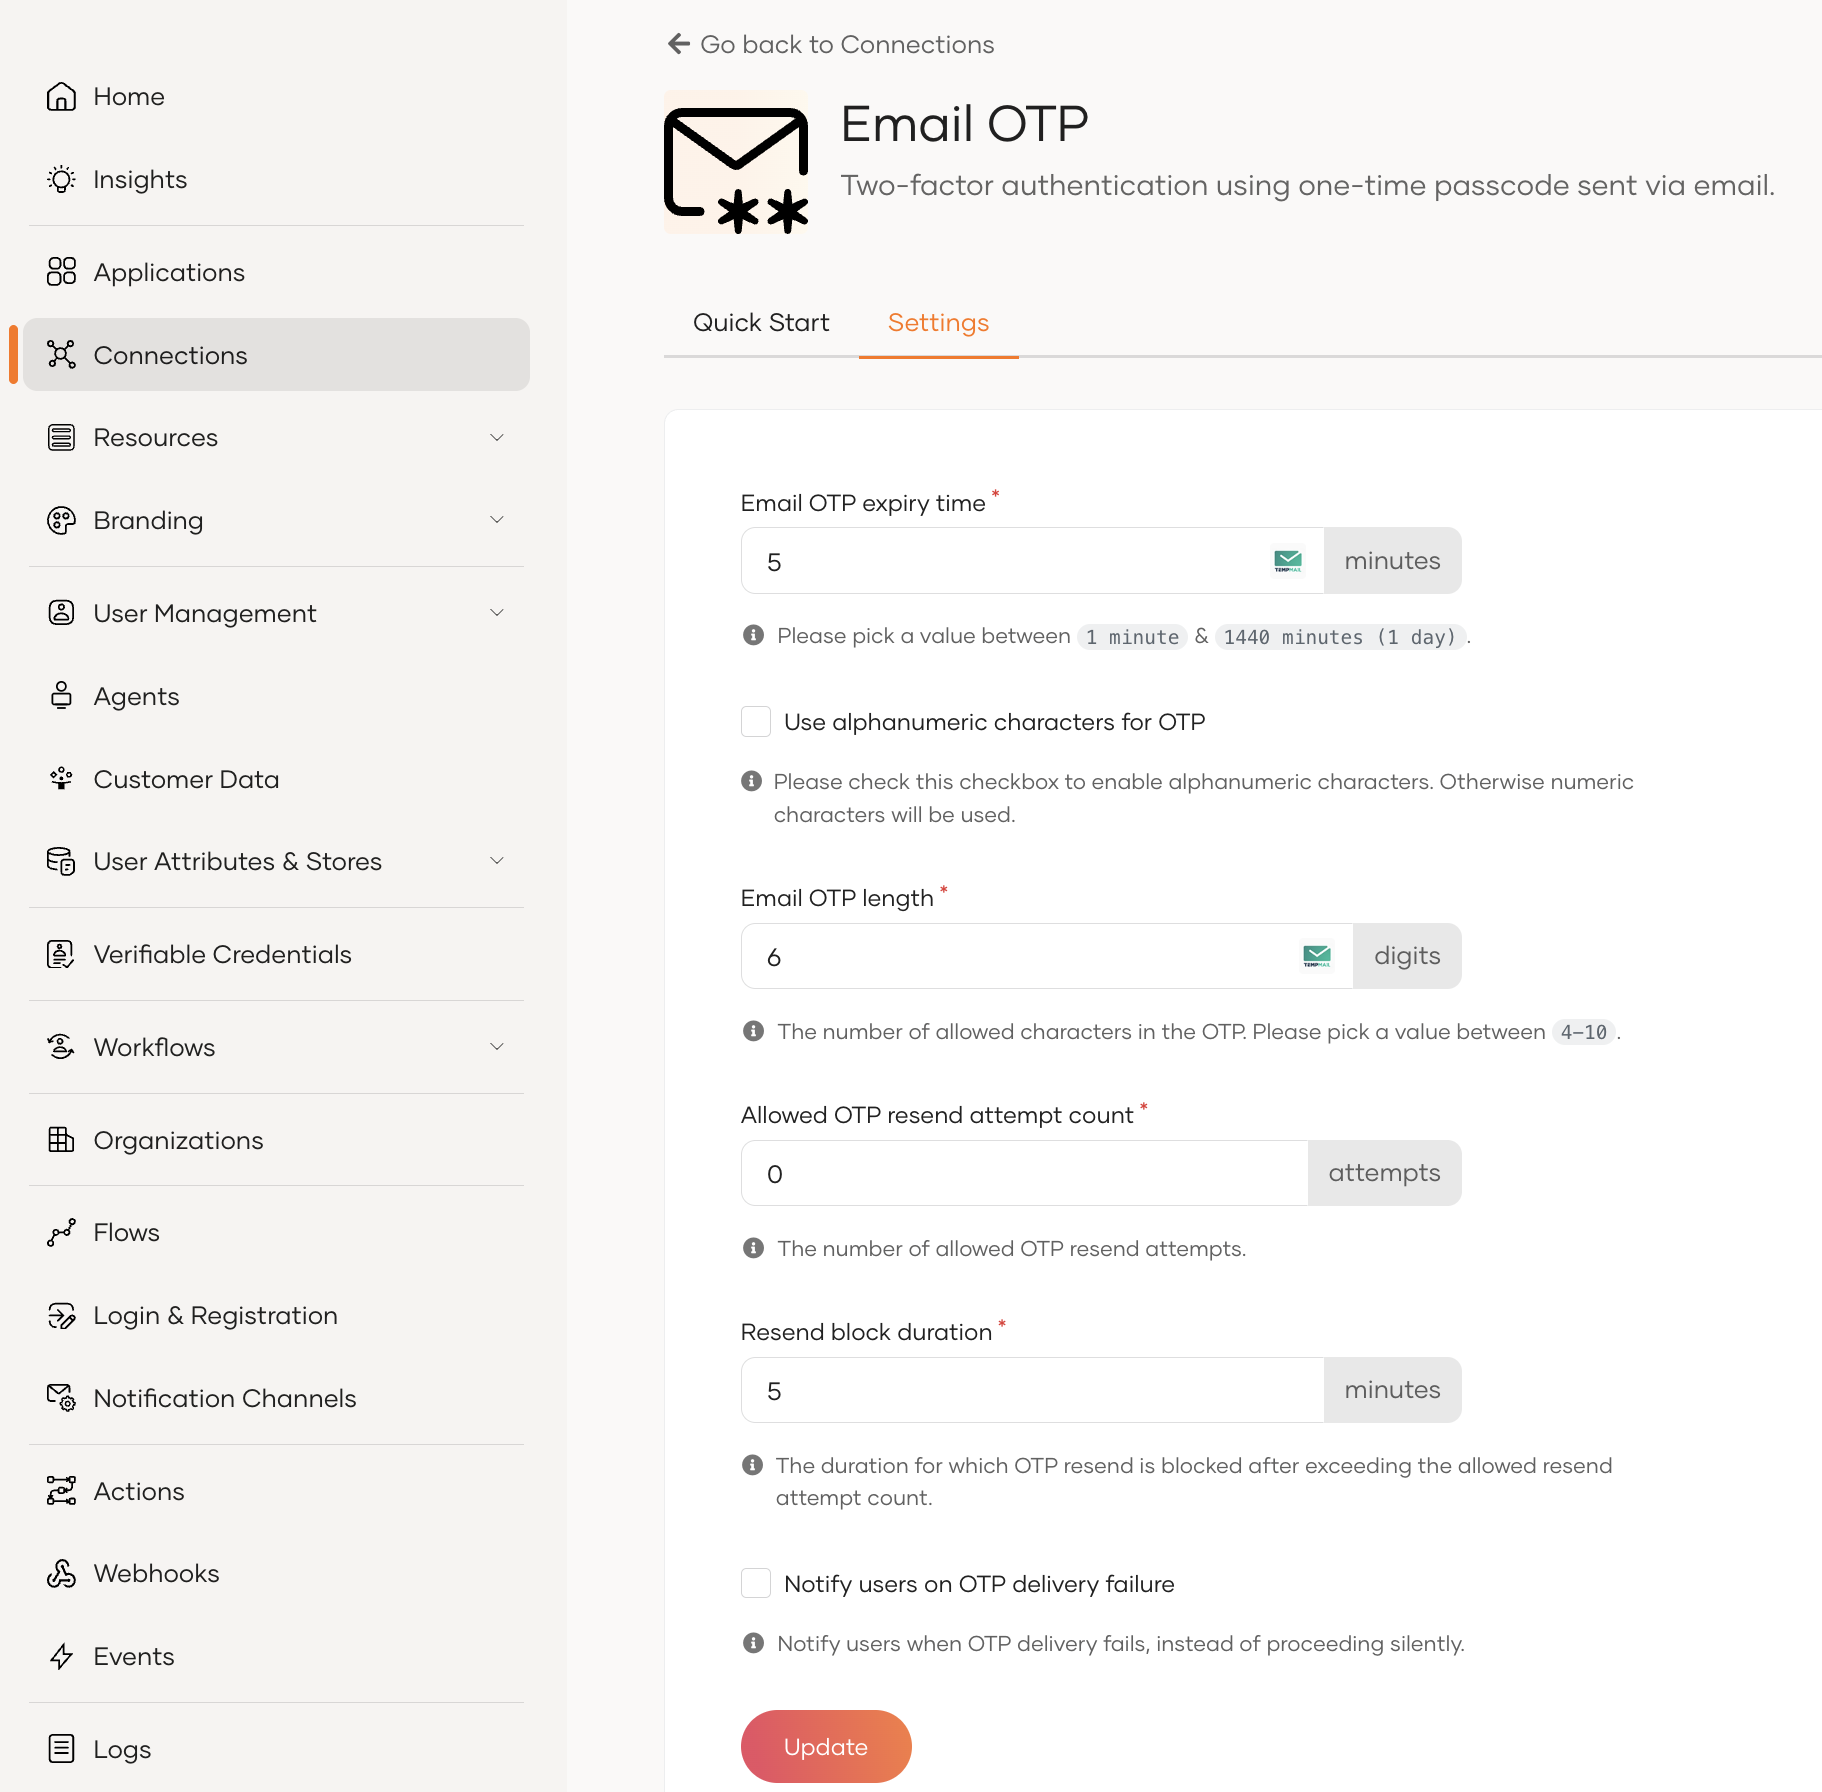
Display provider connection failure messages to end users for the Email and SMS authenticators
Introduces an option to display user-friendly error messages to end users when an error occurs while connecting to the email or SMS provider. This option is disabled by default and can be enabled from the SMS and Email Authenticator configuration sections, as shown below.
Documentation:
Choreo Labs Changelog
- 17 Nov, 2026
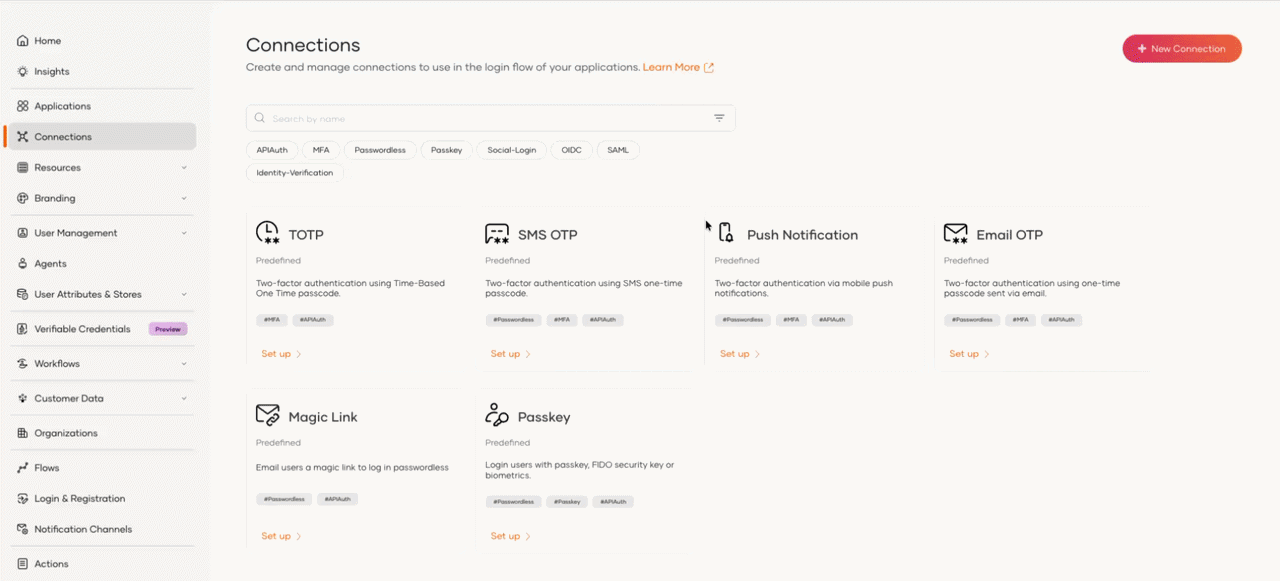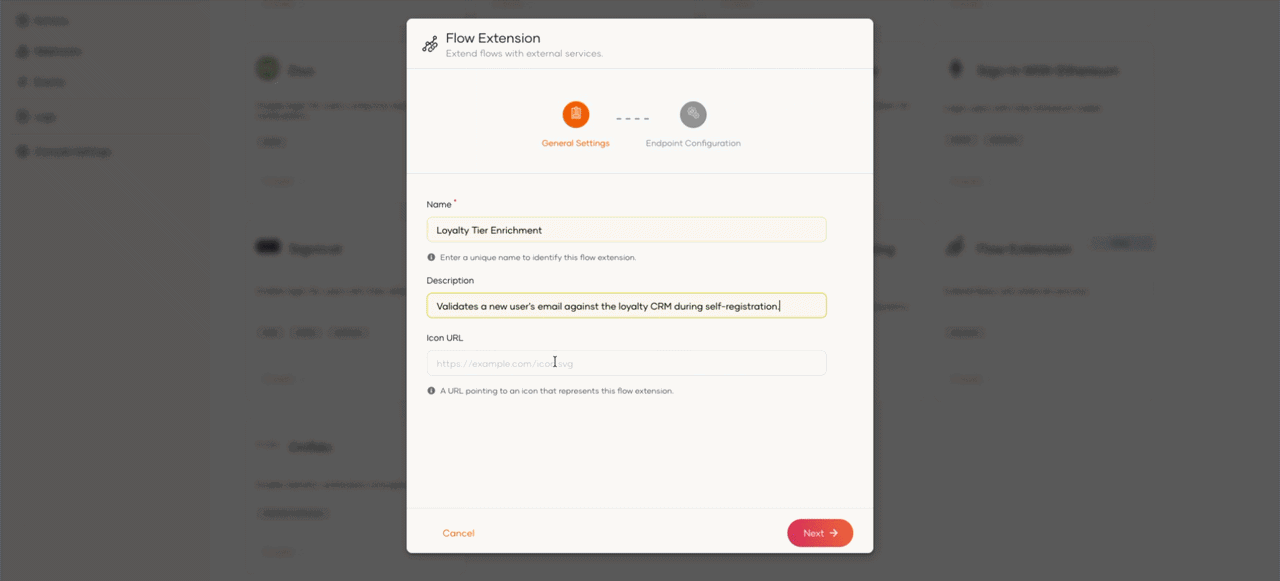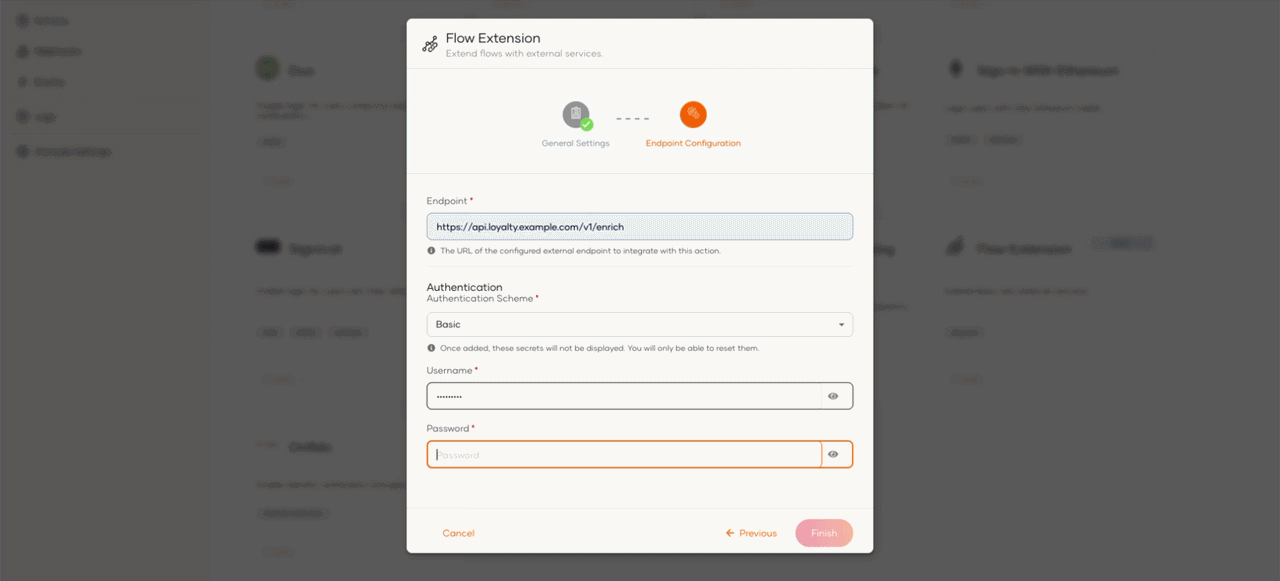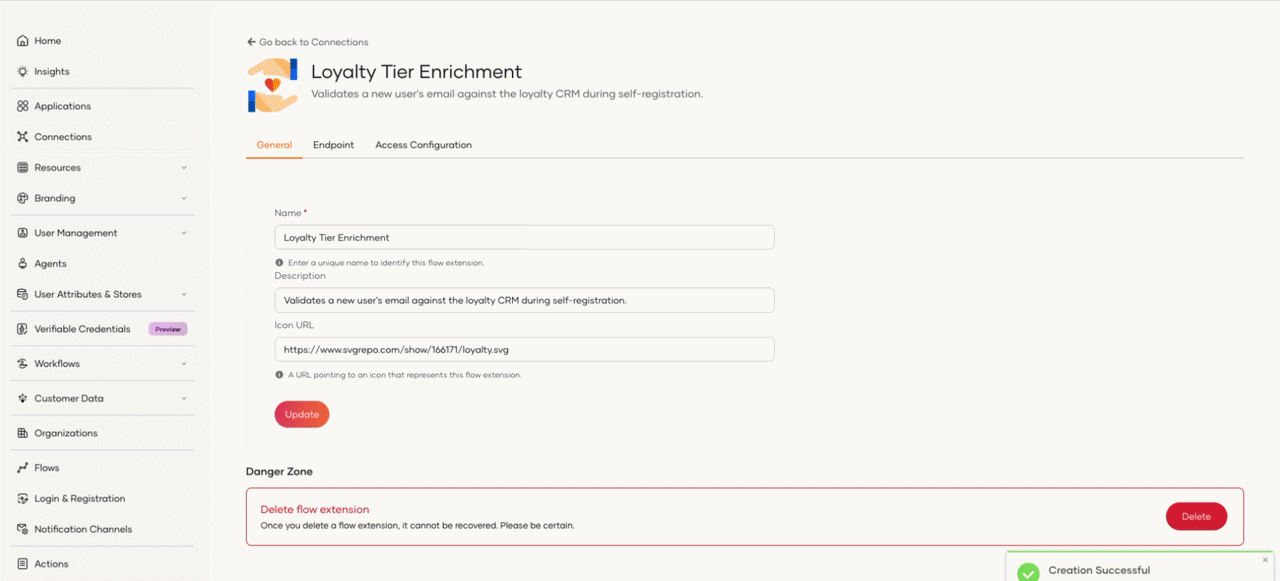
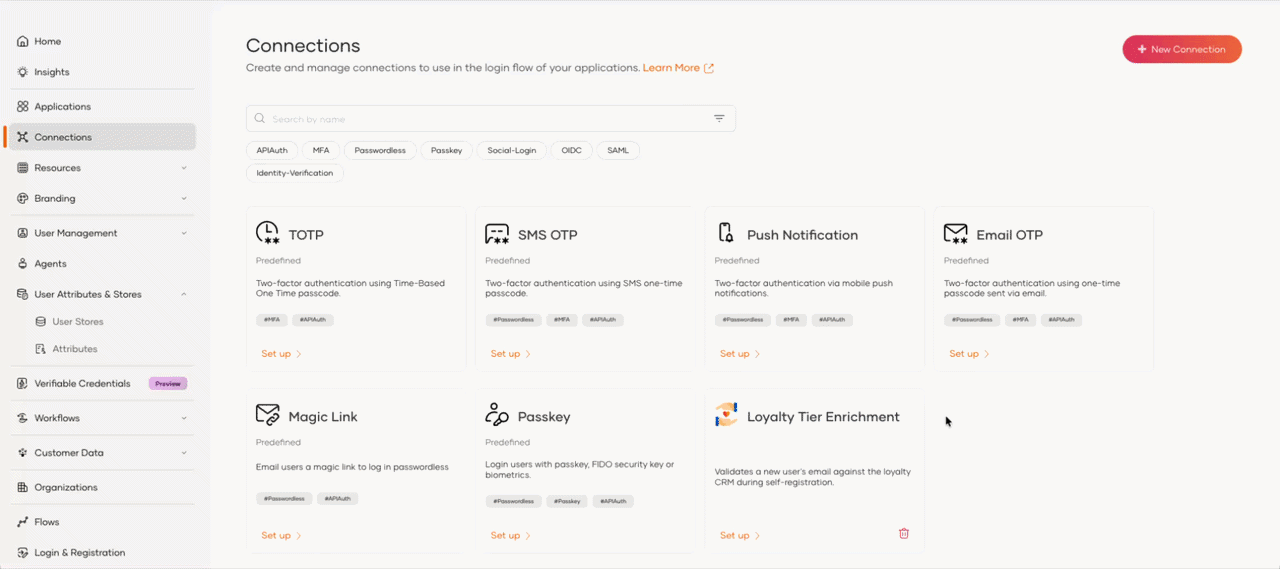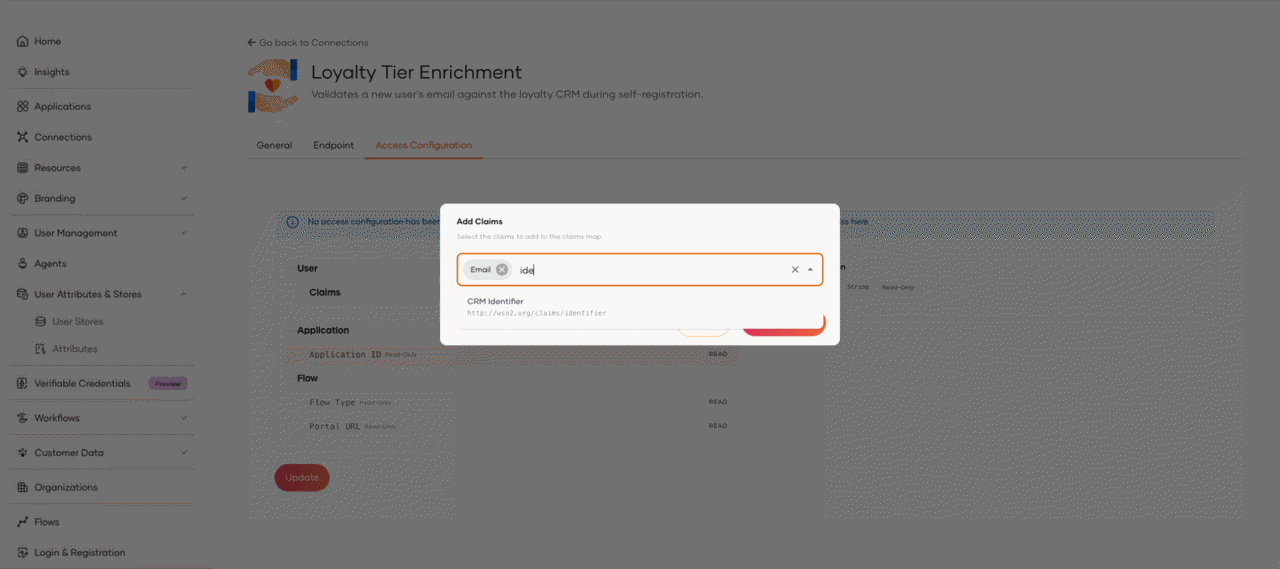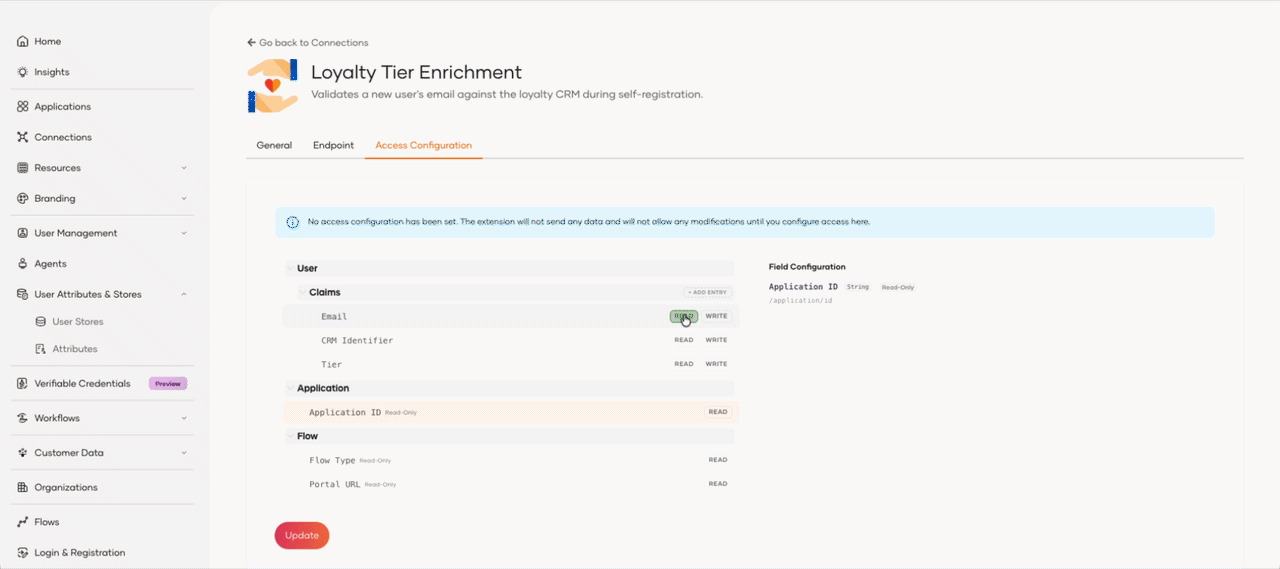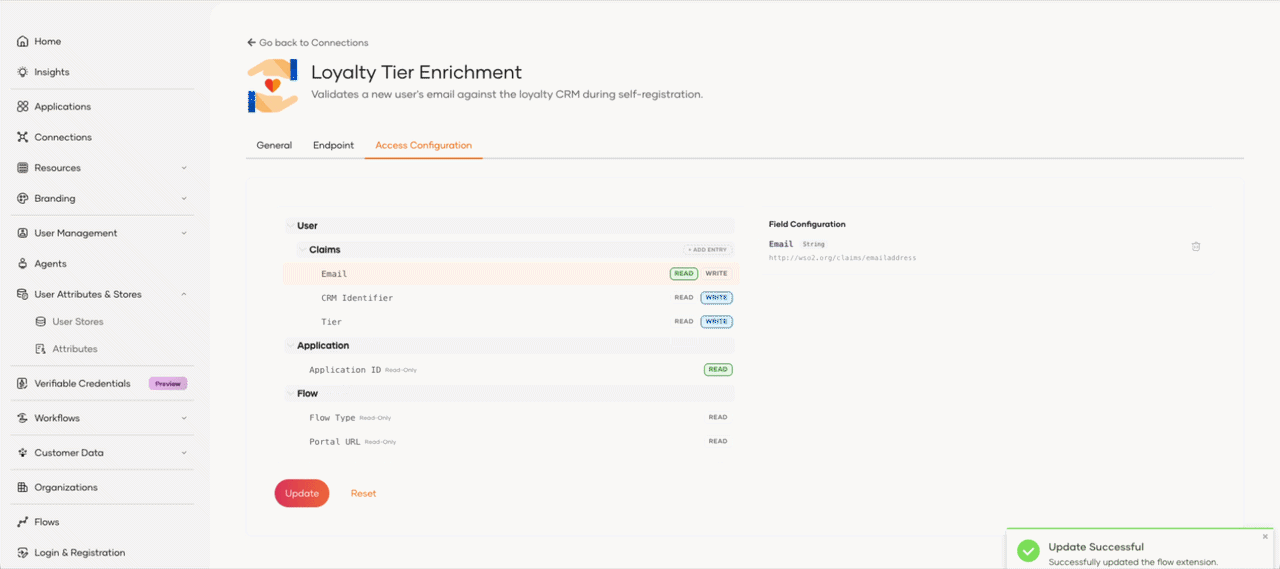
Flow extensions
Flow extensions allow external services to be invoked as part of a self-registration flow, enabling the integration of custom business logic like validation or risk evaluation.
Documentation:
Choreo Labs Changelog
- 17 Nov, 2026
User credential management REST API v2
Introduced a new User Credential Management REST API v2 that lets administrators list and manage user credentials grouped by type, including support for backup codes.
Documentation:
https://wso2.com/identity-platform/docs/apis/end-user-credential-management-v2-rest-api/
Choreo Labs Changelog
- 17 Nov, 2026
Asgardeo rebranded to WSO2 Identity Platform
Asgardeo has been renamed to WSO2 Identity Platform. All product surfaces now reflect the new name. This is a naming change only; no functional changes, and no action is required from existing users.
Choreo Labs Changelog
- 17 Nov, 2026
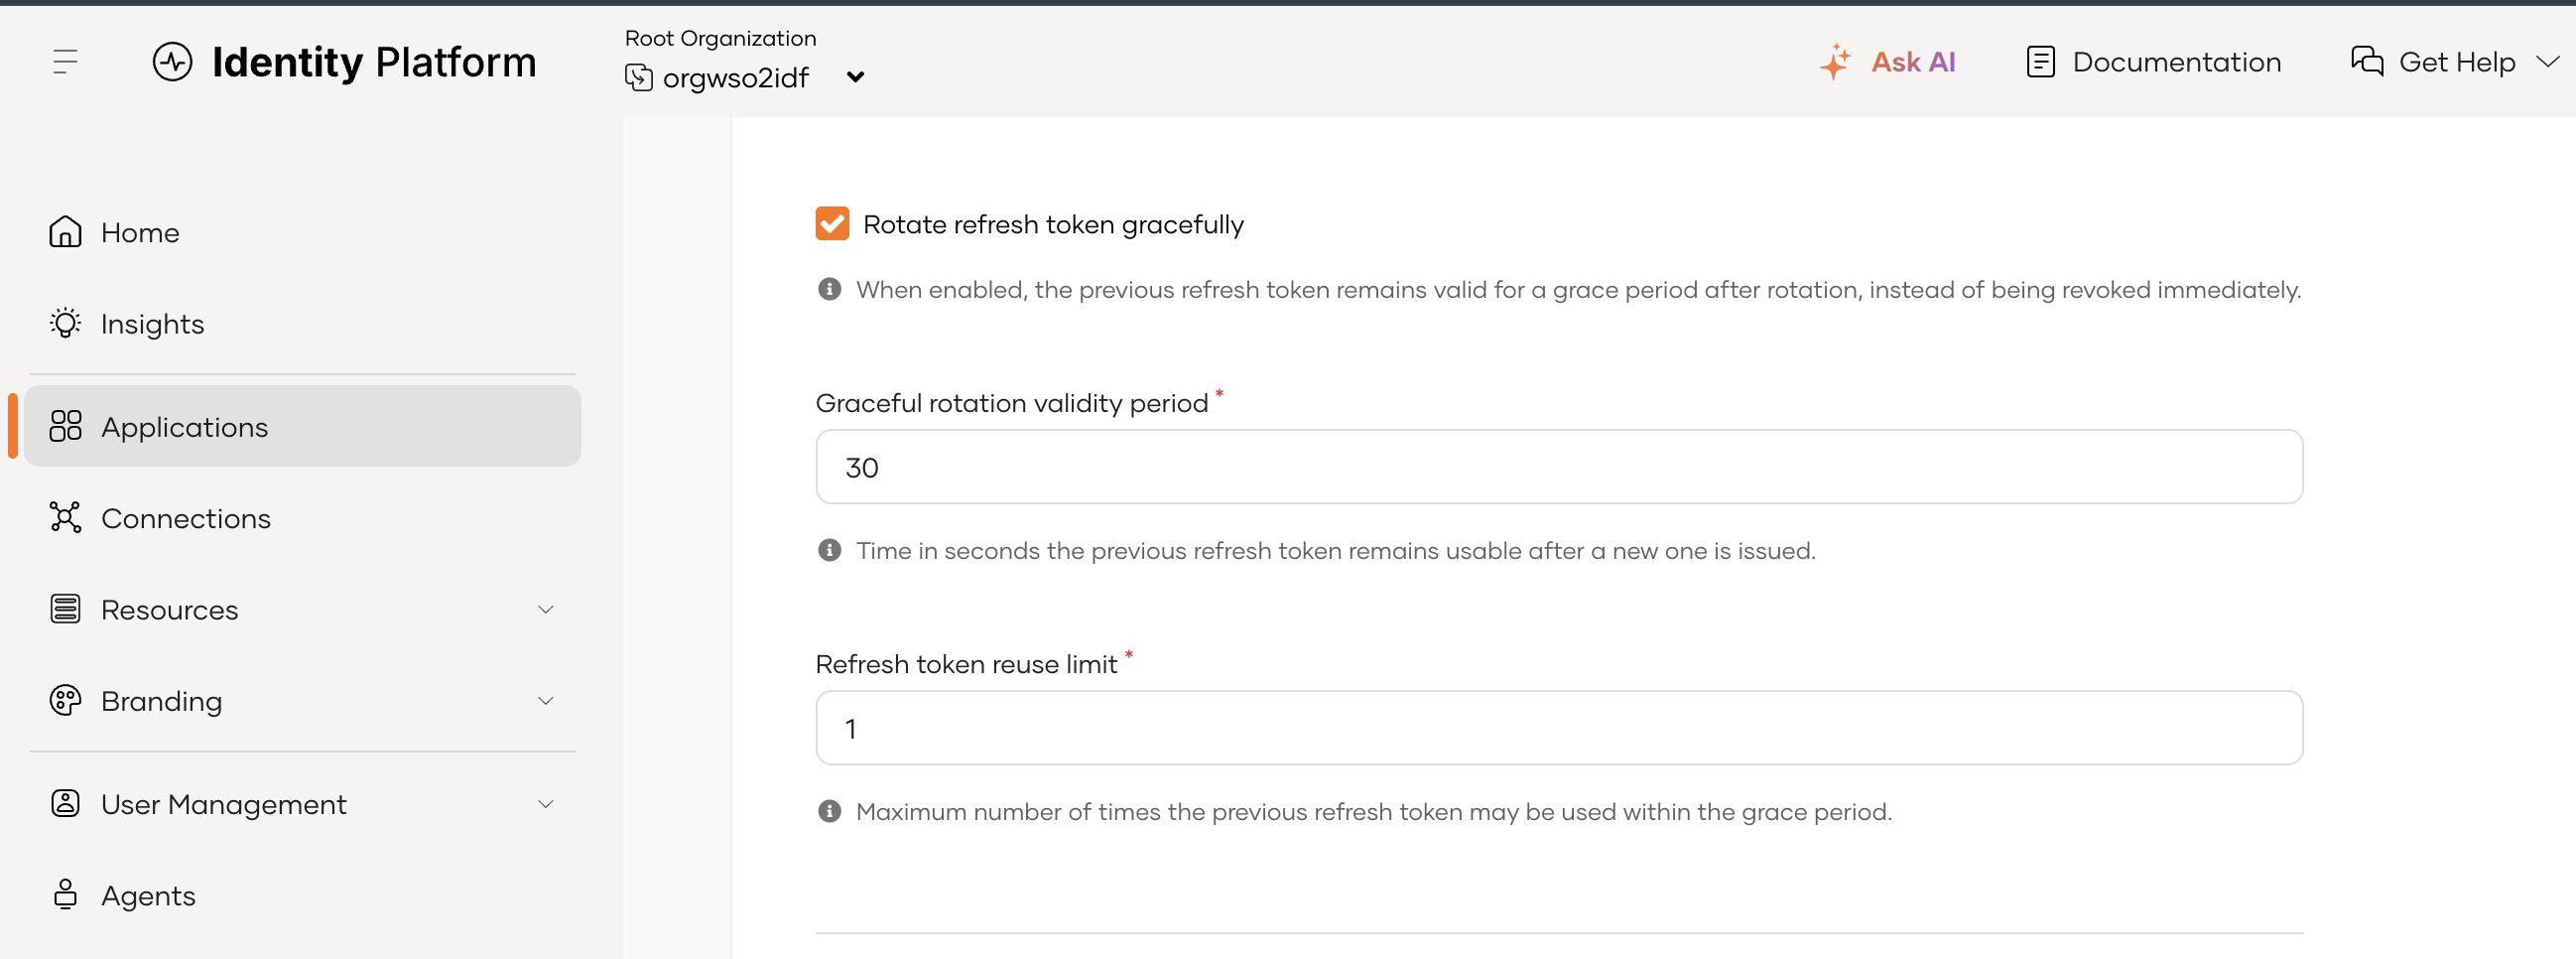
Graceful refresh token rotation support
We are introducing graceful refresh token rotation, allowing old refresh tokens to remain valid for a configurable grace period after rotation, on a per-application basis. This gives client applications a buffer window to complete in-flight requests using the previous refresh token before it's invalidated, reducing failures caused by race conditions during token rotation.
One infrastructure for circular 64, AI law 134, and decree 13
Circular 64, Vietnam's AI Law, and Decree 13 all govern the same banking systems. See why one platform beats three separate compliance programs.
What enterprise buyers are asking for in the age of AI
Most enterprises are increasing AI investment, but few feel mature in deploying it. Field notes from enterprise buying conversations show that the gap often comes down to weak integration, API, and identity foundations, not model or budget limits.
From data silos to AI action: how enterprise Integration unlocks AI ROI
Enterprise AI doesn't stall because the model is wrong, it stalls because it can't reach the systems the business runs on. See why integration debt is the real barrier to AI ROI, and what it takes to close the gap.