AI gateway vs API gateway: Key differences
On this page
An API gateway manages access and traffic to APIs. An AI gateway adds controls for model workloads, such as token accounting, provider routing and model-specific policies. These capabilities can run in separate components or within the same gateway platform.
A chatbot might receive client requests through an API gateway and call model providers through an AI gateway. That is one useful deployment pattern, not a requirement for every AI application. Decide which controls you need first, then where they should run.
AI gateway vs API gateway: The short answer
An API gateway and an AI gateway govern two fundamentally different directions of network traffic. An API gateway manages inbound traffic from clients into your microservices. It works as a reverse proxy that handles basic authentication, rate limiting, and load balancing for standard request and response payloads.
An AI gateway manages outbound traffic from your applications to LLMs and model providers. It tracks token usage, dynamically routes across multiple LLM providers, caches prompt responses semantically, and applies guardrails against AI-specific threats.
They do not operate sequentially, where one gateway hands traffic off to the other. Instead, they govern distinct paths across your architecture:
- Inbound Traffic: A client or web application sends a request to your application backend, a path governed by your API gateway.
- Outbound Traffic: Your application backend calls an external LLM (such as OpenAI or Anthropic) or a self-hosted model, a path governed by your AI gateway.
Consider a website chatbot. When a user sends a message, the browser calls your chat backend through an API gateway only if the backend is exposed as a managed API. Your chat backend then makes an outbound call to an LLM provider through the AI gateway. The API gateway handles client authentication and service traffic while the AI gateway handles token budgeting, prompt guardrails and model routing.
So in a nutshell: API gateways govern how clients reach your services while AI gateways govern how your applications call language models. Production AI systems require both because they manage two entirely different traffic flows.
What is an API gateway?
An API gateway is the centralized entry point for client requests to your backend services. It acts as a reverse proxy that sits between callers and a fleet of microservices, so clients talk to one stable endpoint instead of dozens of internal ones. Instead of every backend service reimplementing these cross-cutting concerns, the gateway handles them centrally:
- Authentication and Security: Handles authentication and authorization via API keys, JWTs, or OAuth so only valid callers reach a service.
- Traffic Management: Controls rate limits and throttling to shield backends from overloads and enforce fair use across consumers.
- Request Routing: Executes routing based on URL paths, HTTP verbs and headers, plus request and response transformation between client and service formats.
- System Infrastructure: Manages load balancing across service instances, SSL termination, and response caching.
For over a decade, this setup worked like a charm because standard web traffic is structured and predictable. You deal with structured JSON or XML, with request and response shapes you can validate against a schema. Observability is framed around requests, latency percentiles, and error rates. Enterprise API gateways that include Choreo API Manager, Kong, NGINX, Apigee, and AWS API gateway were built for this operational model.
The challenge arises when an application integrates a Large Language Model. Standard API gateway plumbing like TLS, authentication and endpoint routing still works. However, LLM traffic introduces an entirely new unit of measurement (tokens instead of requests) and a brand-new threat model that traditional gateways were never designed to inspect.
What is an AI gateway?
An AI gateway is a specialized middleware layer designed specifically for LLM and generative AI traffic. Traditional API gateways process generic HTTP requests without inspecting prompt payloads. An AI gateway recognizes prompts, tracks token consumption, and dynamically selects model providers based on real-time cost, latency, or capability. It gives you one standardized interface in front of many providers such as OpenAI, Anthropic, Mistral AI, and self-hosted models.
Here is what sets it apart from a standard proxy:
- Multi-Model Routing and Failover: Choose among supported deployments and apply bounded retry or fallback rules. Confirm that the replacement model supports the request's format, tool use and output requirements.
- Token Cost Tracking: Meters input and output tokens per team, application, and model, replacing opaque vendor bills with actionable attribution.
- Semantic Caching: Serve cached responses for prompts that are semantically similar, which cuts both latency and repeat token cost.
- Prompt Management and AI Guardrails: Enforces prompt versioning, validates them, masks personally identifiable information, and screens inputs and outputs for unsafe content.
Monitor latency, failures, token usage and attribution at the granularity your application needs. Apply prompt and response controls as part of a broader defense: validation, least privilege and approval for sensitive actions still matter. Filters reduce risk but cannot guarantee that prompt injection will be prevented. The OWASP Top 10 for LLM Applications is a useful baseline for that defense.
Key differences (side by side)
Compare capabilities rather than assuming the two labels describe mutually exclusive products.
| Capability | General API gateway concern | Additional AI workload concern |
|---|---|---|
| Access control | Authenticate clients and authorize API access | Restrict model and provider access |
| Limits | Requests, concurrency and payload size | Input/output tokens and spending policies |
| Routing | Select service endpoints | Select model deployments and compatible providers |
| Reliability | Timeouts, health checks and bounded retries | Model fallback compatibility and streaming recovery |
| Observability | Latency, status and throughput | Token usage, model attribution and estimated cost |
| Data protection | Credential protection and payload controls | Prompt/response handling and sensitive-data policies |
Feature availability depends on the product, version and configuration. For example, Azure API Management documents AI gateway features as extensions of its existing gateway. Direction of traffic is a property of the deployment, not a universal definition of either category.
Do they compete or complement?
AI gateways do not replace API gateways. They are complementary because they govern entirely different directions of traffic, not because they form a sequential pipeline.
An API gateway sits at the edge of your infrastructure to manage inbound client traffic to your backend services. An AI gateway sits between your internal application backends and external model providers to manage outbound LLM calls.
When building an AI-enabled application, the architectural choice is how your application calls language models:
- Direct provider integration: the application owns routing, usage attribution, limits and safety controls. This can suit a small deployment when those responsibilities are implemented and maintained explicitly.
- Shared gateway integration: multiple applications use a common place to apply selected controls. This reduces repeated integration work but adds a dependency whose availability, configuration and behavior must be operated.
A gateway is not a substitute for application authorization or output validation. Choose the boundary that gives your team reliable enforcement with manageable operational work.
Architectures also incorporate a third layer which is the MCP (Model Context Protocol) Gateway. As autonomous AI agents start calling your backend tools, an MCP gateway governs that inbound agentic traffic, enforcing authentication, authorization, and throttling on the tools agents are allowed to invoke.
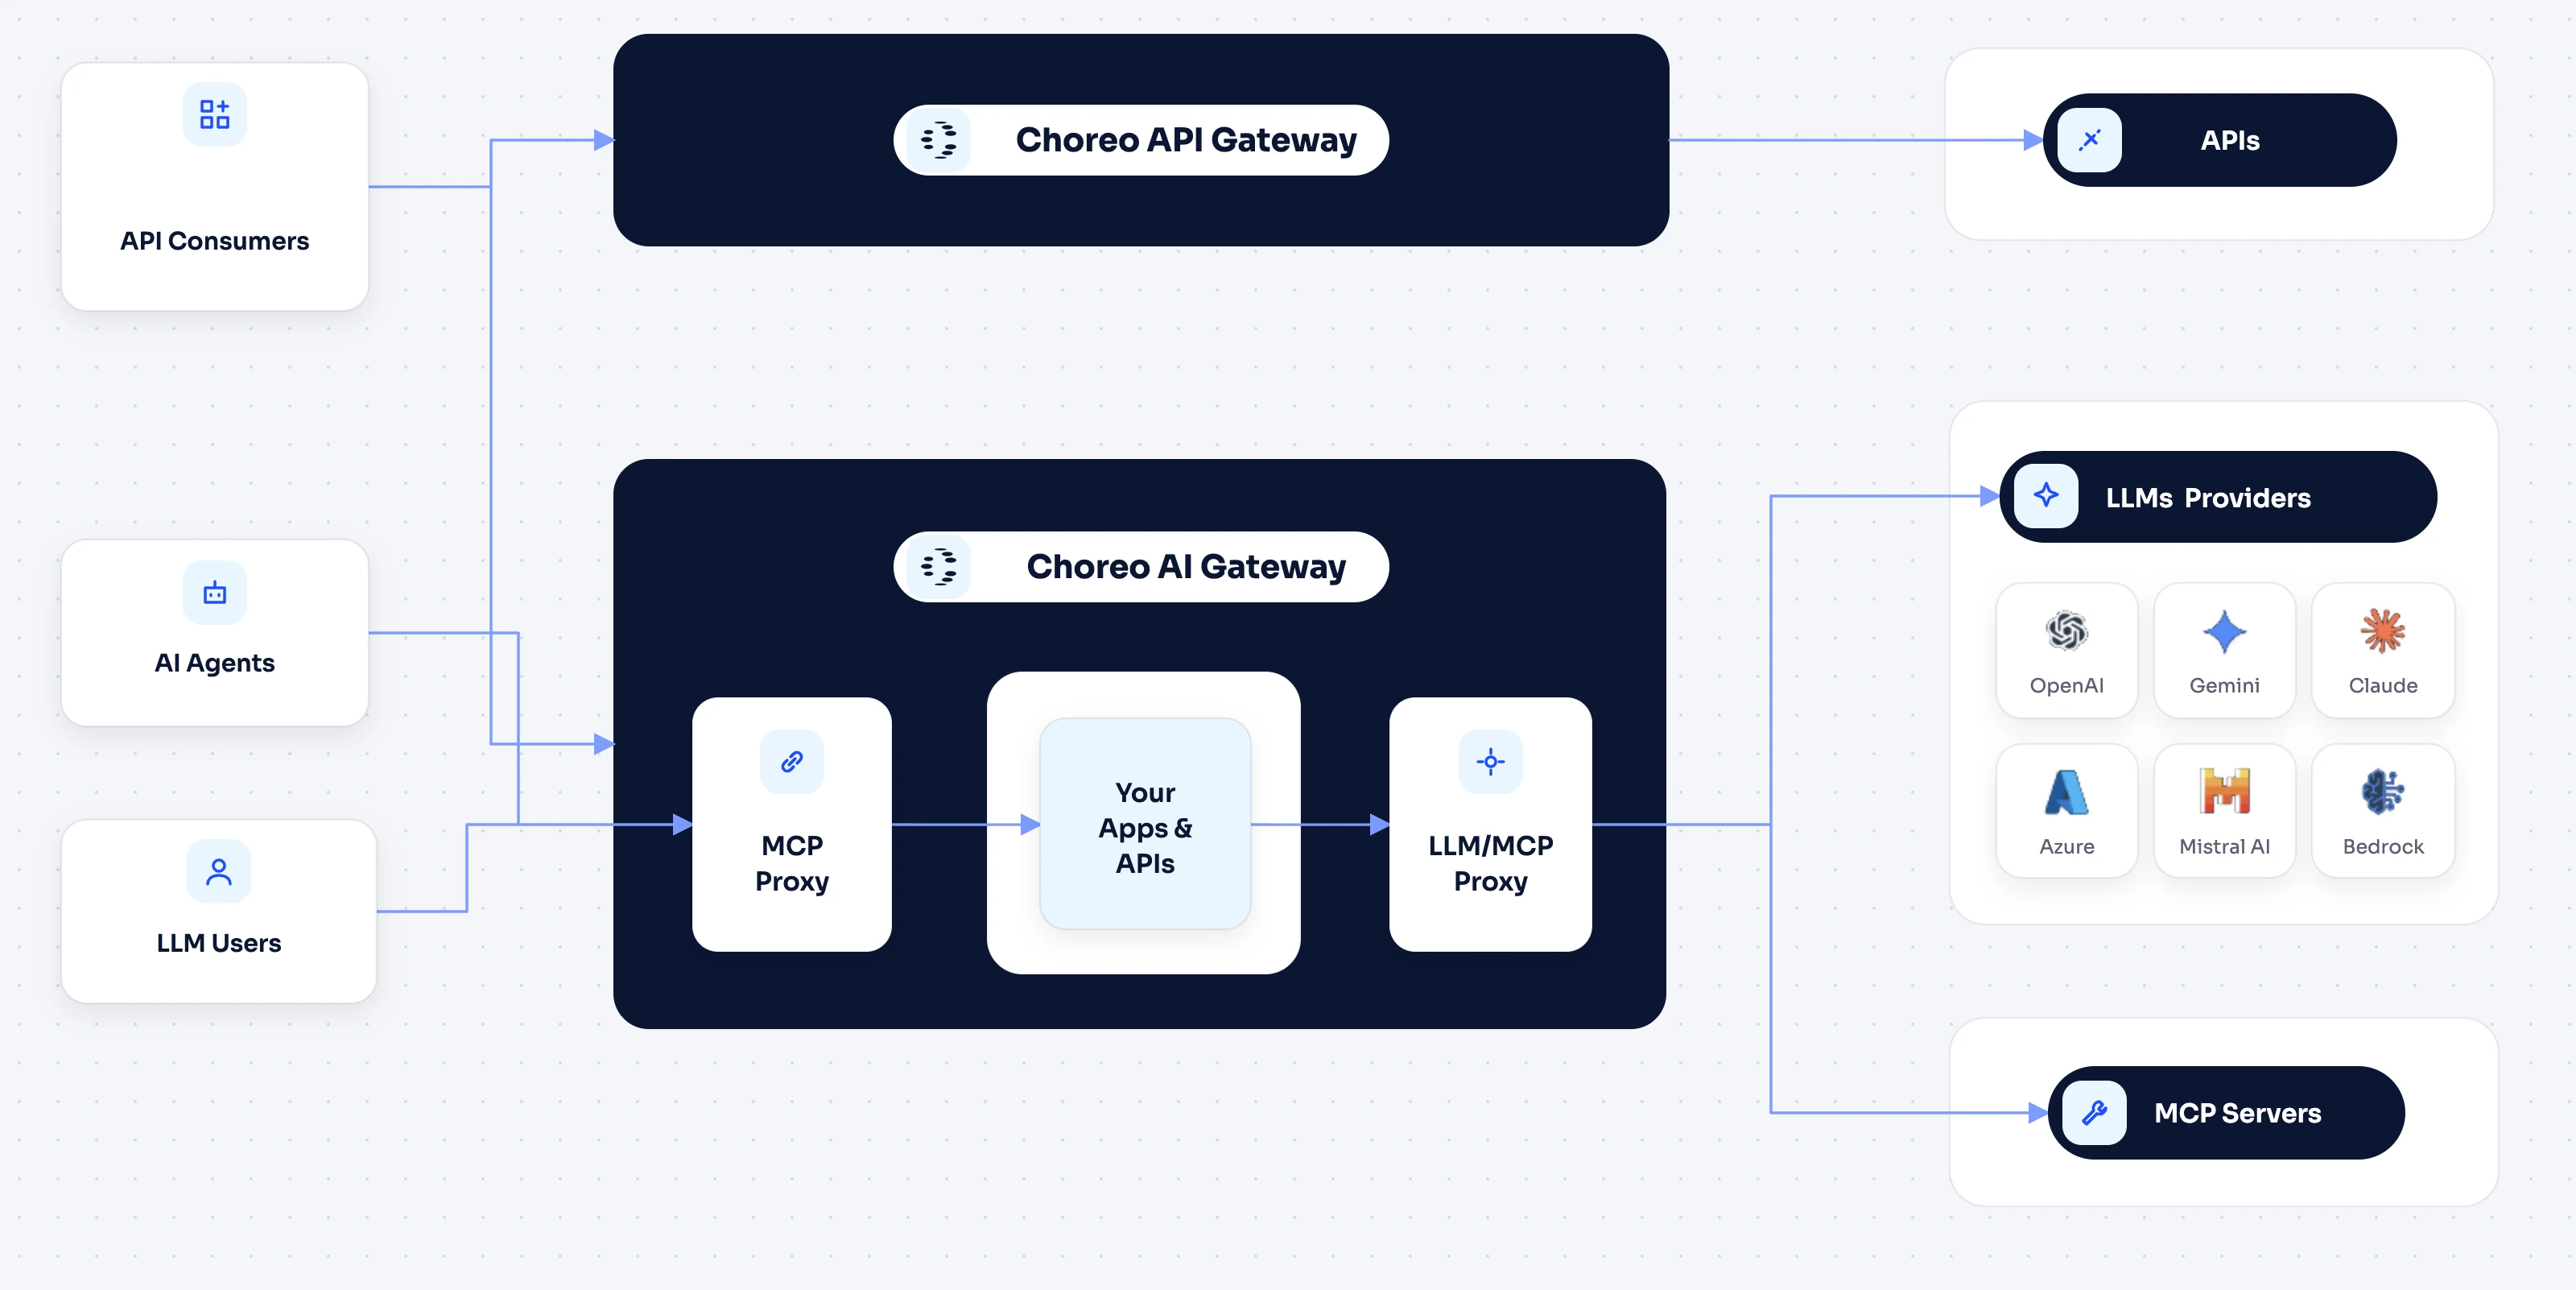
The above diagram portrays the dual traffic paths:
- Inbound client requests routed to services via the API gateway.
- Outbound application requests routed to model providers via the AI gateway.
The golden rule of modern architecture: API gateway for service traffic, AI gateway for model traffic and MCP gateway for agent traffic. Three specialized tools under one unified governance model beats stretching a standard gateway far past its purpose.
When to use which (decision guide)
Add a gateway when shared controls solve a concrete operating problem: repeated authentication logic, inconsistent limits, fragmented usage reporting or complex routing across applications. The number of services alone does not determine whether the additional component is worthwhile.
Add an AI gateway when:
- Multi-Model Operations: Multiple application teams are calling different model providers. You need intelligent, unified routing based on real-time cost, latency and model capabilities rather than hard-coding provider logic into every application.
- Cost Management: AI spend is opaque or growing rapidly. You need granular token metering, cost estimation, and vector-based semantic caching to gain total spend attribution.
- Compliance and Security: Your applications process regulated data in finance, healthcare or government. You need centralized audit trails, PII masking and strict guardrails to prevent prompt injection and data leaks.
- Production Scale: AI features are integrated into production applications serving external users, making ad-hoc token management and unmonitored vendor API keys an unacceptable reliability risk.
You can defer adopting an AI gateway if your setup is limited to a single application calling one model provider or an early proof-of-concept. In these early stages, calling the provider SDK directly from your application keeps the architecture simple until multi-model or governance requirements arise.
For implementation requirements, use the AI gateway comparison. If you are replacing an existing model proxy, the LiteLLM alternatives guide includes a migration test worksheet. If your primary concern is agent access to tools, compare MCP gateways and proxies.
How Choreo API Management provides both
Most vendors specialize in one side of this comparison. Choreo API Management takes a different approach by shipping both API gateway and AI gateway under a single unified control plane, allowing standard service traffic and your generative AI workloads to share one identity and governance model instead of two disconnected stacks.
Here is how Choreo API Management bridges both worlds:
Traditional API: Delivers complete API lifecycle management. From OpenAPI or AsyncAPI design, automated governance policies, versioning, and publishing APIs as products. Its control plane doesn't just manage Choreo gateways, it manages Kong, AWS, Azure and Envoy gateways together.
AI gateway umbrella: Choreo API Management tackles modern AI traffic through two complementary components:
- Outbound LLM Gateway: Handles multi-model routing and automatic failover across OpenAI, Azure AI, AWS Bedrock, Anthropic and Mistral AI. It enforces safety guardrails (semantic prompt validation and PII masking), semantic caching and provides token-based rate limiting with department-level chargeback.
- Inbound MCP Gateway: Governs autonomous agentic traffic by creating MCP Proxies on top of existing MCP servers, enforcing strict authentication, authorization and throttling on agent calls.
You get one unified platform with 100% open source, deployable across self-hosted, hybrid or SaaS environments from a recognized Leader in The Forrester Wave™: API Management Software, Q3 2026. For enterprise architects, adopting an AI gateway doesn't have to mean gluing on a separate tool with a whole new policy language and its own audit trails.
Conclusion
API gateways manage your standard service traffic, AI gateways handle LLM traffic and MCP gateways step up as autonomous agents come online. If you already have an API gateway guarding your perimeter, add an AI gateway the moment token costs, multi-model routing or safety guardrails demand more than generic proxying.
If you would rather run all three layers under one unified control plane instead of stitching together separate tools, see how Choreo API Management unifies API, AI and MCP traffic under one roof.
Frequently asked questions
What is the difference between an API gateway and an AI gateway? An API gateway controls client access to your applications and microservices, handling standard HTTP authentication, load balancing and request rate limits. An AI gateway controls outbound requests from your applications to language models, managing token consumption, cost attribution, provider failover and prompt guardrails.
What is an AI gateway? An AI gateway is a control plane for managing interactions with large language models. It gives developers a single interface to connect with vendors like OpenAI, Anthropic or self-hosted models while providing centralized controls for token budgeting, semantic caching, PII redacting and prompt safety inspection.
Do I need an AI gateway? You should adopt an AI gateway if your organization manages multiple LLM providers, requires spend attribution across teams, handles regulated data in prompts or serves external production users. You can wait if you are building an early proof-of-concept with a single application calling one model provider directly.
Should I route LLM calls through an AI gateway or call provider SDKs directly? Calling provider SDKs directly works for small prototypes, but it creates architectural blind spots as applications scale. Directly integrated SDKs leave organizations vulnerable to unmonitored API spend, lack prompt caching to reduce token costs, and provide no centralized mechanism to stop prompt injection or enforce compliance policies across models. Routing outbound calls through an AI gateway enforces those controls before requests leave your network.